Most IT advice treats every business the same way: keep it running, keep it patched, back it up. A law firm is judged by a different standard, because two of its risks have no real equivalent elsewhere. Miss a filing deadline because the VPN was down and you are not explaining an outage, you are explaining a possible malpractice claim. Lose control of a mailbox and you have not simply had a data breach, you have had a privilege breach.
Almost everything below follows from those two facts.
Downtime has a date attached to it
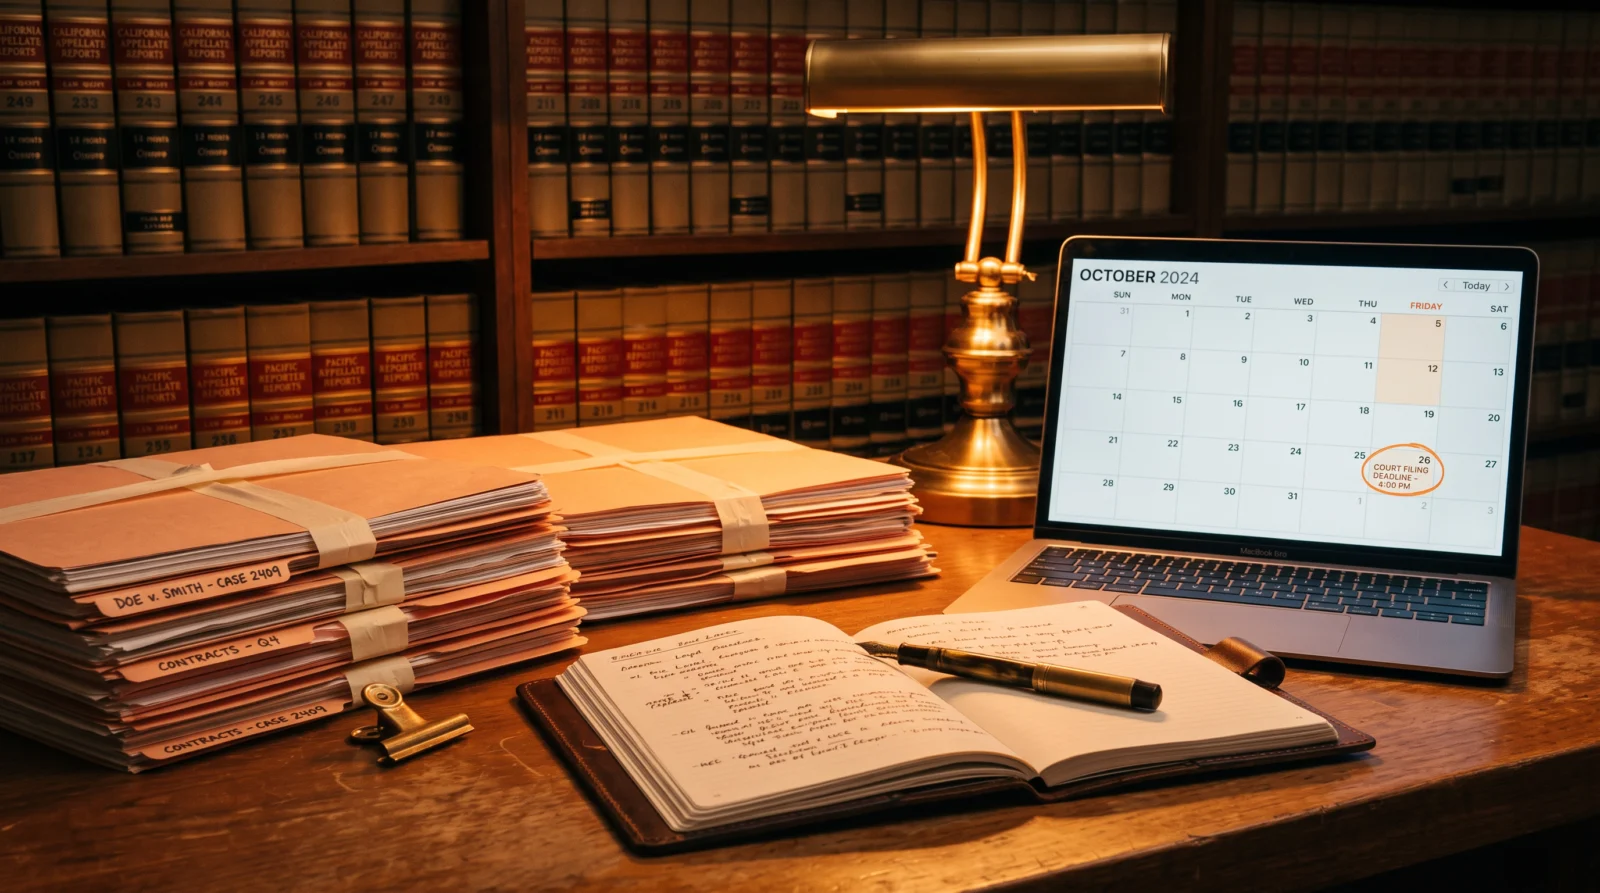
In most businesses an afternoon of downtime costs productivity. In a practice it can cost a cut-off. Electronic filing portals close at a fixed time, limitation periods do not move because a file server did not come back, and nobody has ever persuaded a court with the argument that the IT was down.
That changes how recovery should be specified. The question stops being how long can we tolerate being down, and becomes what is in the diary for the next forty-eight hours. In practice:
- Know which deadlines sit inside your recovery window. A four-hour recovery target is comfortable in a quiet week and useless on the morning of a filing.
- Keep a route to the portal that does not depend on your office. A laptop with cellular tethering and a tested remote login is a cheap insurance policy.
- Diaries and limitation dates belong in something replicated, not in a practice management database sitting on one server in a cupboard.
- Paper still has a role. A printed list of the next two weeks of critical dates costs nothing and has rescued more firms than any appliance.
Confidentiality is a professional obligation, not a policy
Every business says it takes client confidentiality seriously. For a firm it is a rule of professional conduct, with a duty to make reasonable efforts to prevent disclosure and a widely adopted expectation that competence now includes understanding the technology you use. A compromised mailbox is not just an IT incident; it is privileged material in somebody else’s hands, with reporting obligations and client notifications attached.
The controls that matter most are unglamorous and well understood:
- Phishing-resistant multi-factor authentication on every mailbox, partners included. Business email compromise is the single most common way a firm loses money and confidentiality at the same time, and we went through exactly how it works in The Phishing Trap.
- A password manager, and no reuse. Court portals, land registries, e-filing systems and counsel portals each need their own credentials. The options, free and paid, are in Password managers: free is fine, until the auditor arrives.
- Encryption that you understand the limits of. Full-disk encryption protects a laptop left on a train. It does nothing against a credential that has been phished, which is covered in Data Safeguards: From Storage to Transit.
- Ethical walls that exist in the file system, not only in the conflicts policy. If a matter is walled off, the permissions should enforce it.
The software nobody else supports
This is where most general IT providers come unstuck. A practice does not run on Office alone. It runs on practice management, time recording, billing and document assembly, and those applications behave in ways that surprise people who have never supported them.
TimeMatters, Timeslips, Amicus, Abacus, HotDocs and the e-filing tools each have their own quirks: database back ends that need specific maintenance, client components that are fussy about Windows updates, document templates that break when a Word version changes, and upgrade paths that have to be sequenced rather than jumped. An engineer meeting these for the first time learns them on your time and at your risk.
Three practical consequences:
- Test the applications, not just the server. A restore that brings back a database but not a working client installation has not restored anything useful.
- Patch deliberately where vendors certify slowly. Some legal applications lag behind operating system updates. That is a reason to plan the sequence, not a reason to stop patching.
- Synchronise the calendars properly. Court dates and client meetings that live only on one machine are a risk; they should reach phones and tablets reliably, wired or wireless.
Your clients are starting to audit you
Corporate clients increasingly send outside counsel guidelines and security questionnaires, and they expect evidence rather than assurances: encryption in place and demonstrable, multi-factor authentication enforced, access reviewed, incidents reported within a stated window, data held in named jurisdictions, subcontractors disclosed.
Firms that can answer those questionnaires quickly win work from firms that cannot. It is worth assembling the answers once, keeping them current, and treating that document as a business asset rather than a chore.
Most IT vendors overlook the detail that matters most in a practice: how the case management and billing software actually behaves on Windows. The firms that have fewest problems are the ones whose provider already knew.
A short list worth working through
- Multi-factor authentication on every mailbox, with partners and finance on hardware keys or passkeys.
- A tested restore of the practice management system, including the client application, not only the database.
- A documented way to reach the filing portal when the office is unavailable.
- Mobile devices enrolled and remotely wipeable, because they hold client correspondence.
- Ethical walls enforced in permissions and reviewed when matters change.
- A current answer to the security questionnaire your next corporate client will send.
We have supported practices for over twenty years, and the pattern rarely changes: the technology is ordinary, but the consequences of getting it wrong are not. If you would like to talk about how your firm is set up, our Legal IT support page explains how we work with legal clients.